Create Verifier Template
A verifier template (shown as Receive credential configuration in the UI) defines which credentials you want to receive from a customer in a single verification flow. You can create a different template for each use case.
Assume you want to onboard a new customer. For your Know Your Customer (KYC) use case, you need to receive credentials to prove:
- The Deed of Incorporation of the customer
- The LPID of the customer
- The Tax Registration Statement of the customer
What is a verifier template?
A verifier template is the configuration that defines which credentials, and which attributes of those credentials, you want to receive from a customer in a single verification flow. You create one template per use case - for example, one for KYC onboarding and a different one for a mortgage application - and reference it by key when you start a verification request.
Open the verifier templates list
- Open Settings.
- Under Verifier, select Templates.
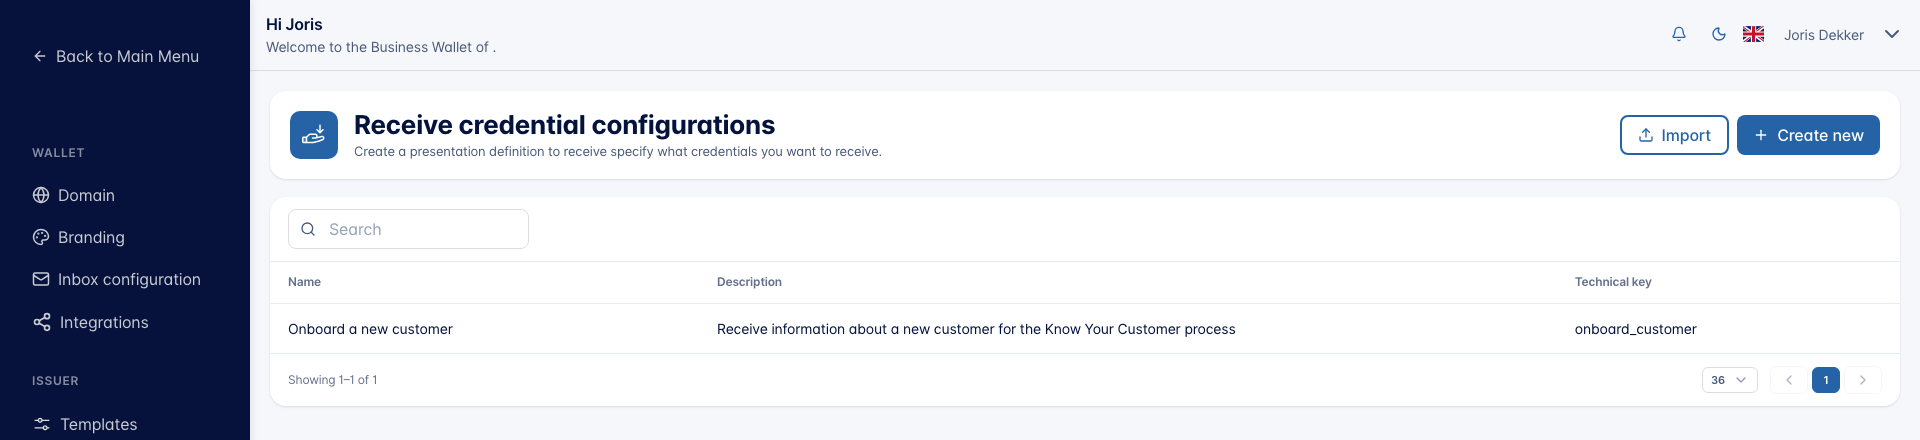
The table lists the existing templates with their Name, Description, and Technical key. Use the Search box above the table to filter the list by name, description, or technical key.
From here you can:
- Create new: start from a blank template
- Import: import a verifier template that was previously exported
Click a row to open and edit an existing template.
Verifier template form
A verifier template is grouped into four sections: Technical details, Technical configuration, Policies, and Configure Credentials.
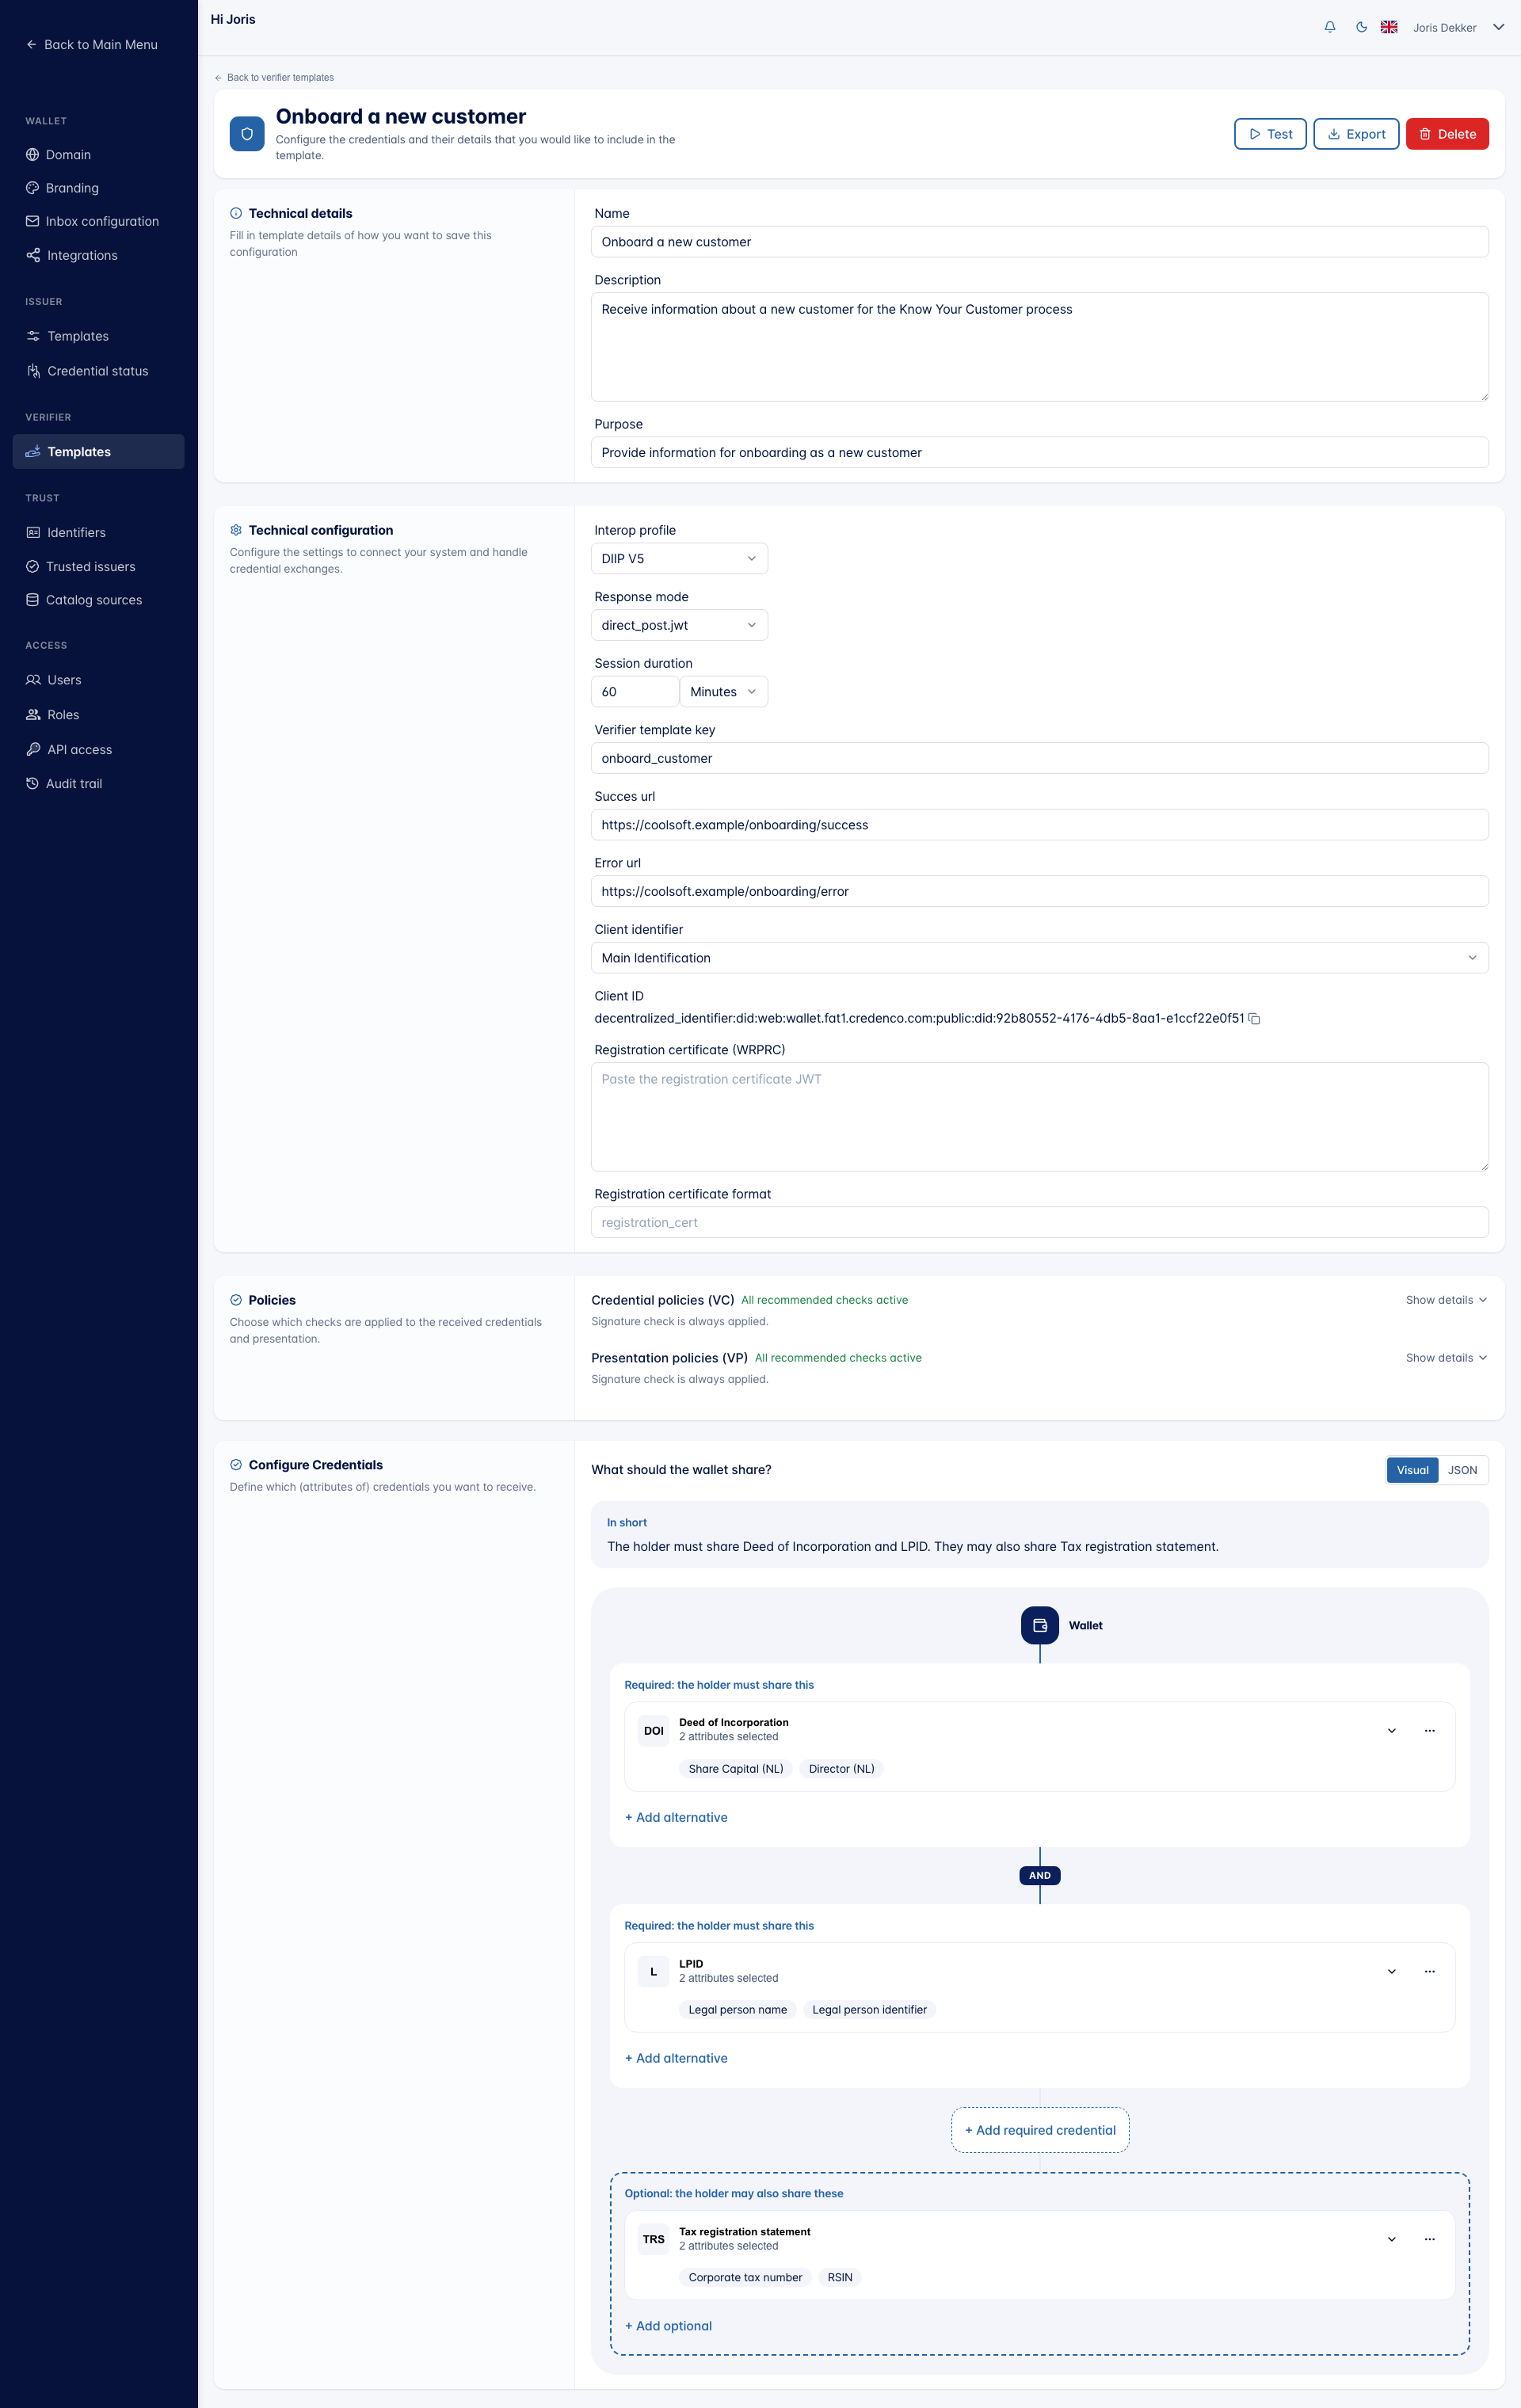
Once a template is saved, the top-right actions let you Test it, Export it to JSON, or Delete it.
Technical details
Describe what this template is for.
- Name (required): A name for your own use, to recognise the template in the list. Holders do not see it.
- Description: An internal note on what the template is used for. Holders do not see it.
- Purpose (required): The reason for the request, shown to the holder in their wallet when the wallet supports it. Explain in plain words why you ask for these credentials.
Technical configuration
Configure the protocol details used during the credential exchange.
-
Interop profile (required): The interoperability profile that defines the protocol versions used between the verifier and the wallet. Pick from:
DIIP V3DIIP V4DIIP V5HAIP
See the DIIP specification for details on the DIIP profiles, or the OpenID4VC High Assurance Interoperability Profile for HAIP.
-
Response mode (optional): How the wallet sends its answer back. Leave this empty to let the calling application decide. Pick from:
direct_post: the wallet posts its answer to the Business Wallet.direct_post.jwt: the same, but the answer is encrypted. Choose this when the wallet requires an encrypted response; some wallets, such as France Identité, refuse to answer otherwise.dc_apianddc_api.jwt: the answer comes back through the browser, for requests made with the Digital Credentials API. The.jwtvariant is encrypted.
-
Session duration (optional): How long a verification session started from this template stays valid. Enter a number and pick Minutes, Hours, or Days. The value must be between 1 minute and 30 days; the default is 60 minutes.
-
Verifier template key (required): A unique key for this template. Pass this key to the Universal OIDC4VP API to identify which template to use.
-
Success URL (required): The URL the user is navigated to after the credential(s) are successfully received.
-
Error URL (required): The URL the user is navigated to when something went wrong receiving the credential(s).
-
Client identifier (required): The identifier used to authenticate the verifier to the wallet. Pick one of the identifiers configured under Settings → Identifiers.
noteOnly DID and X.509 identifiers can be used as a client identifier. JWK identifiers are not supported.
-
Client ID prefix (only for an X.509 client identifier): How the verifier's client ID is formed. Leave it on Default, or pick
x509_san_dnsorx509_hash. Machine-to-machine requests requirex509_hash. -
Client ID (read-only, shown once the template is saved): The client ID the wallet sees for this template. Copy it with the copy button and give it to a holder who wants to answer your requests automatically; they add it to their trusted contact.
-
Registration certificate (WRPRC) (optional): The relying party registration certificate you received from your national registrar, pasted as a JWT. It is sent to the wallet as
verifier_info. Some national wallets, such as the German EUDI Wallet, require it for PID requests. Leave it empty if the registrar issued none. -
Registration certificate format (optional): The format of the registration certificate in
verifier_info, at most 64 characters. Leave it empty to useregistration_cert; change it only when a registrar asks for another value.
Policies
The Policies section decides which checks are applied to the credentials and the presentation you receive. Checks marked Recommended are switched on by default.
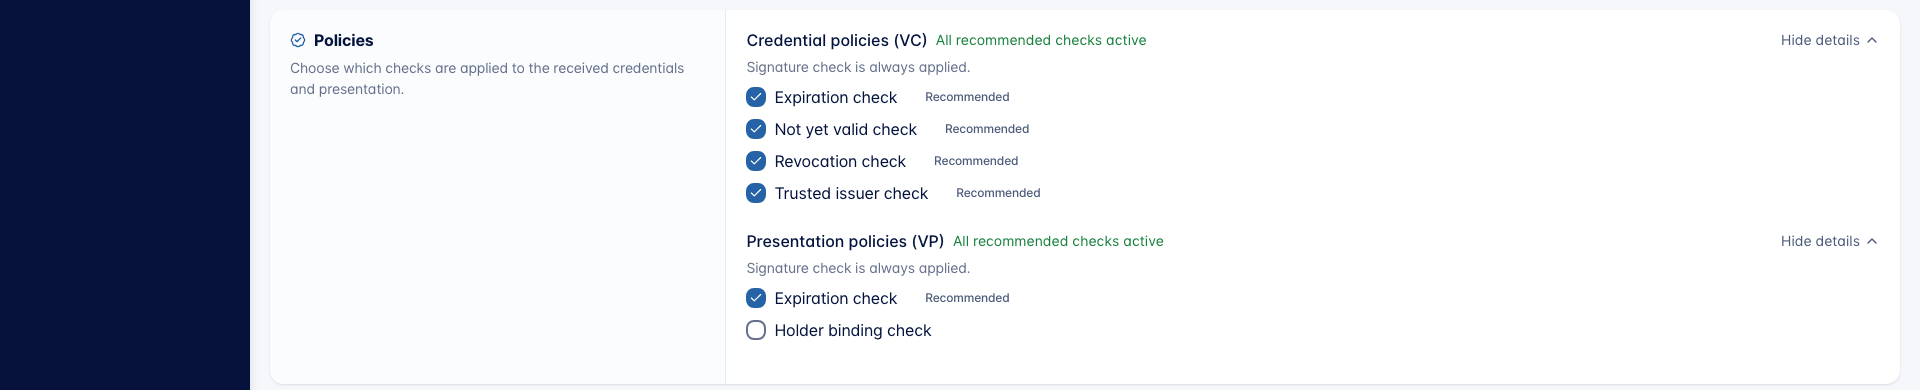
Each group shows a summary, either "All recommended checks active" or "N recommended checks not active". Click Show details to open a group and change the individual checks.
The signature check is always applied to both the credential and the presentation. It cannot be switched off.
Credential policies (VC)
Checks applied to each individual credential you receive.
- Expiration check (recommended): Checks that the credential has not expired based on its validity date.
- Not yet valid check (recommended): Checks that the credential is already valid and not dated in the future.
- Revocation check (recommended): Checks that the credential has not been revoked by the issuer.
- Trusted issuer check (recommended): Checks that the credential's issuer is on the list of trusted issuers. Maintain that list under Settings → Trusted issuers.
Presentation policies (VP)
Checks applied to the presentation as a whole.
- Expiration check (recommended): Checks that the presentation has not expired.
- Holder binding check: Checks that the presentation was submitted by the same party the credential was issued to.
Configure Credentials
The Configure Credentials section decides what the wallet is asked to share. Under What should the wallet share? you choose between the Visual builder and the JSON view of the same request (see Edit the query as JSON).
Click Choose a credential to add the first credential.
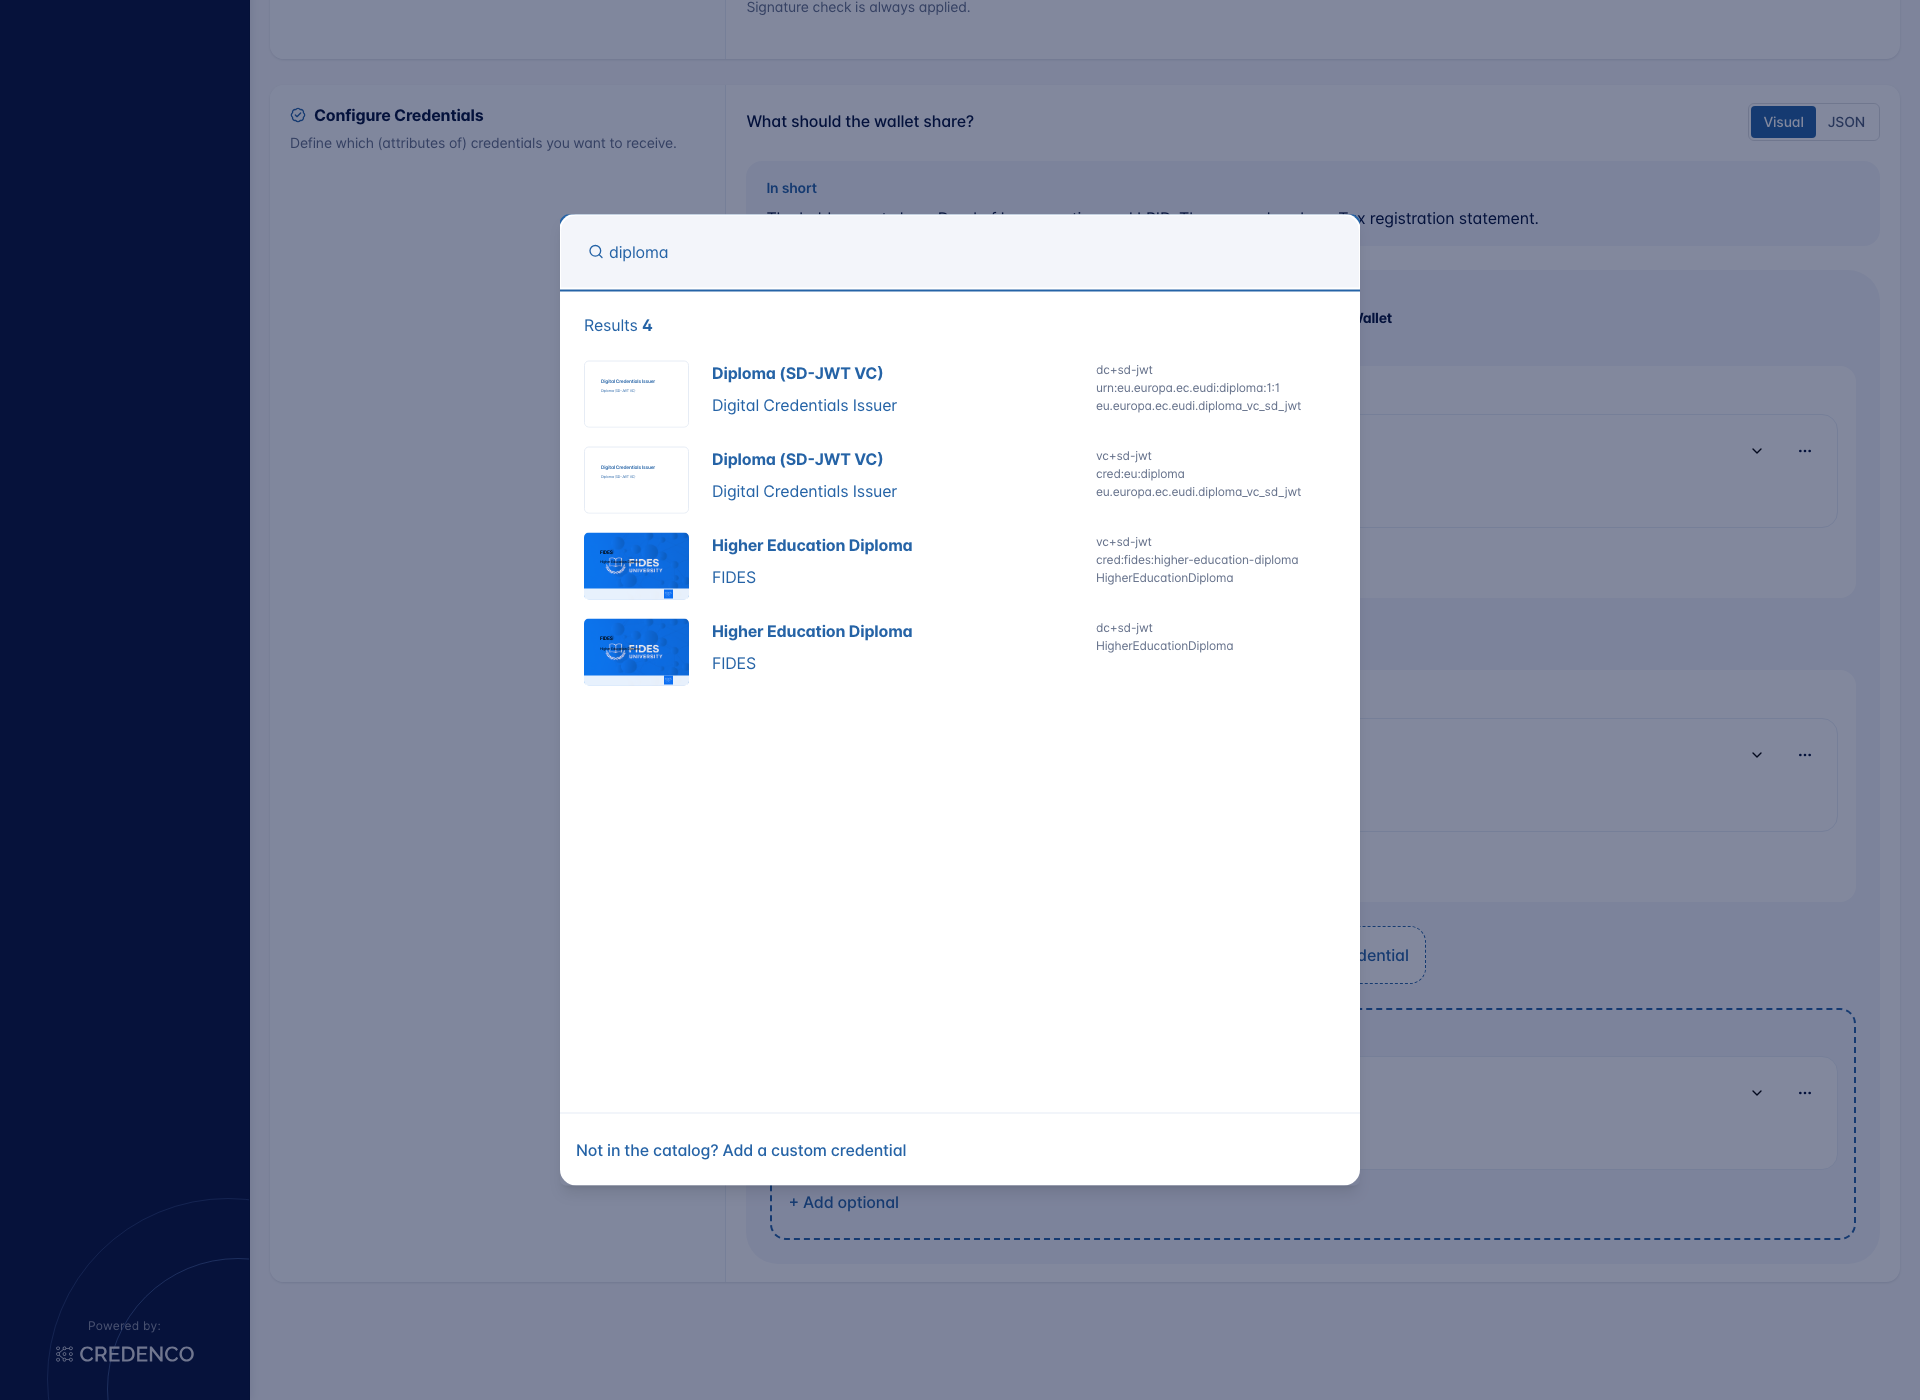
Search the catalogue and click a credential to add it. Each result shows the credential name, the issuer, its format and its type or identifier. If the credential is not in the catalogue, click Not in the catalog? Add a custom credential at the bottom of the list and enter its format and type yourself.
The In short box above the cards summarises the request in plain words, for example "The holder must share Deed of Incorporation and LPID. They may also share Tax registration statement."
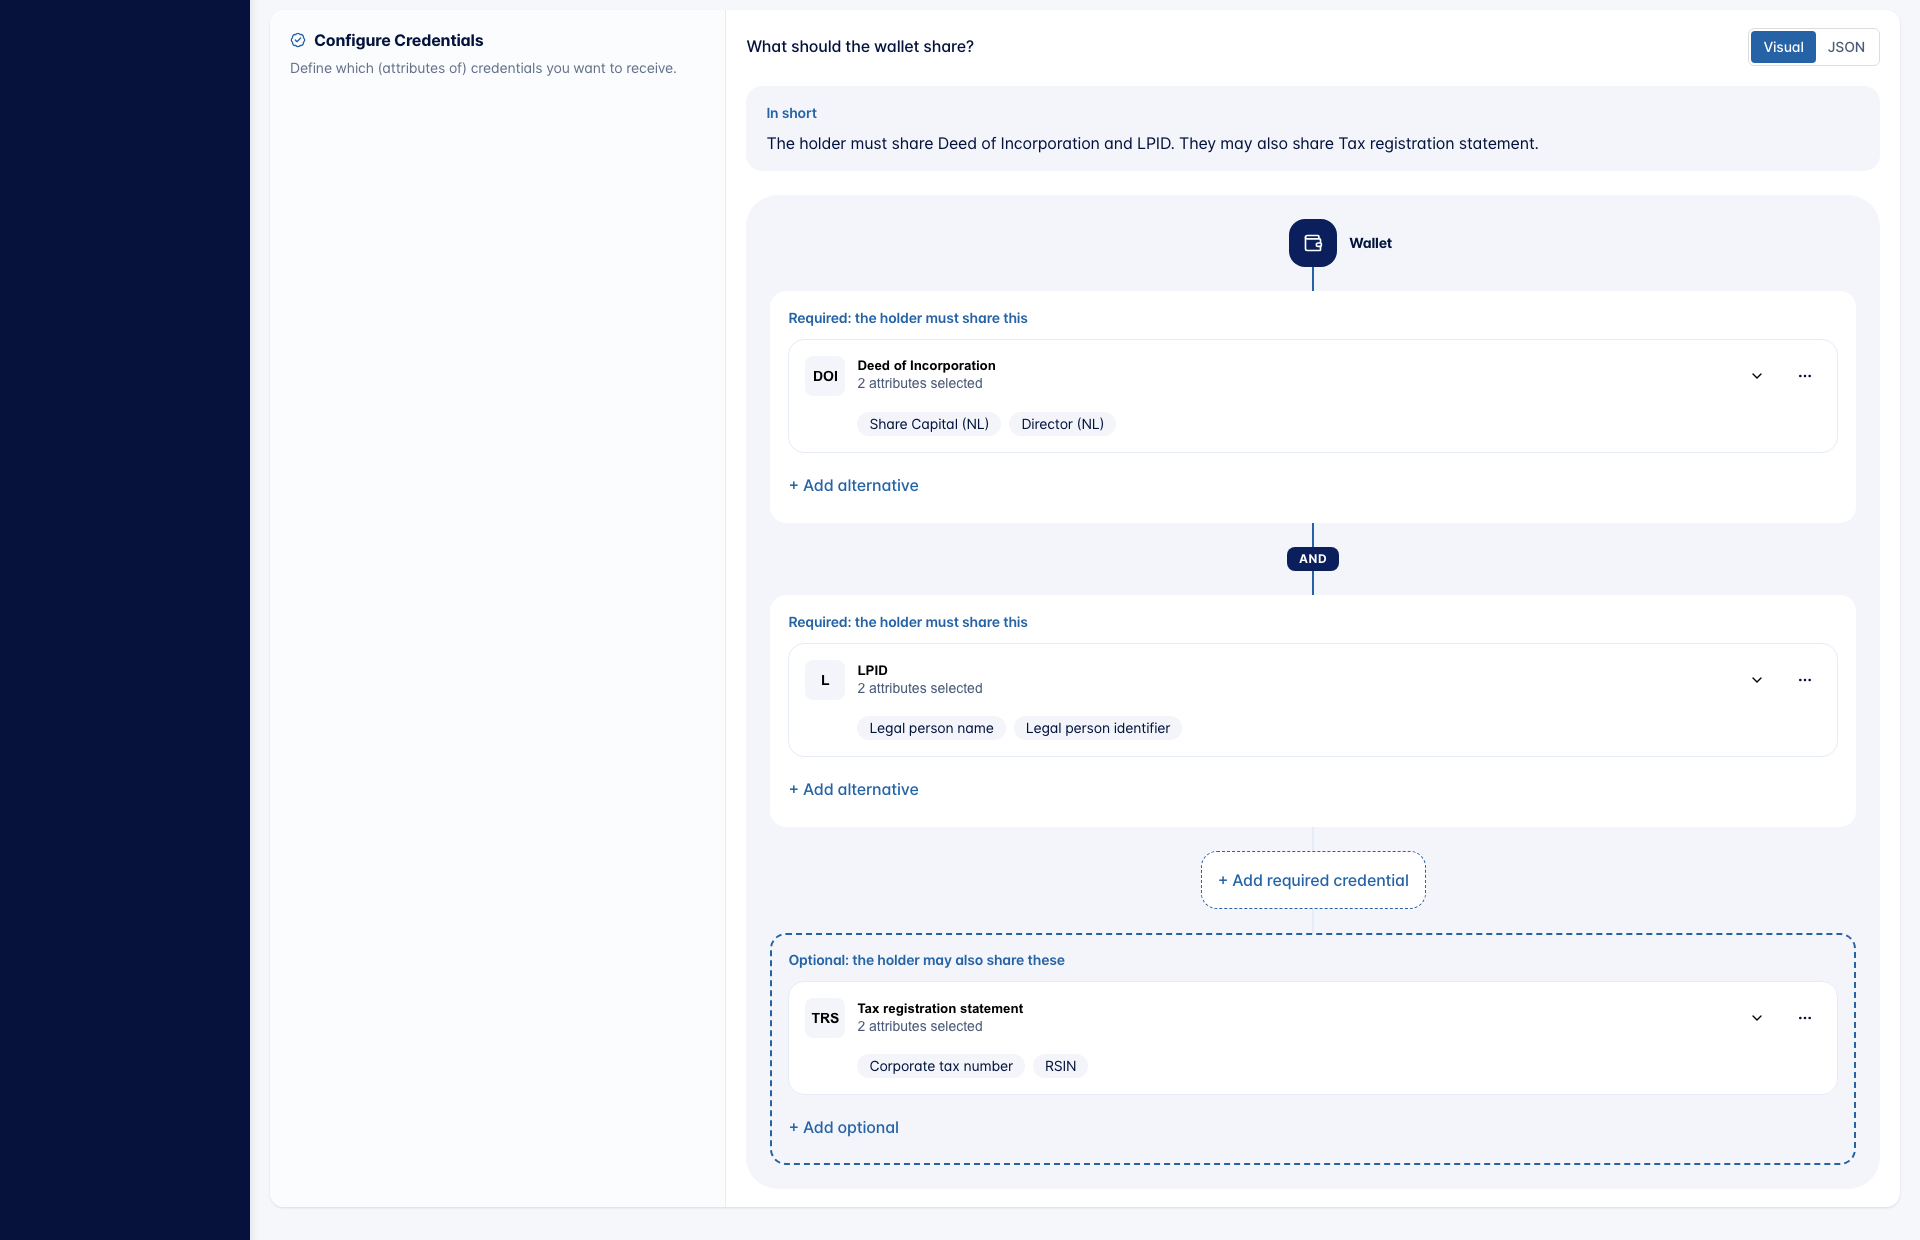
Required and optional credentials
Credentials sit in two lanes under Wallet:
- Required: the holder must share this: every card in this lane must be provided. Click + Add required credential to add another required credential; the cards are joined by AND.
- Optional: the holder may also share these: credentials that are nice to have. Click + Add optional to add one.
On a required card, click + Add alternative and pick another credential when the holder may answer with either one. The lane then reads Required: the holder shares one of these and the cards are joined by OR; for example, a Deed of Incorporation or a Student ID.
Open the … menu on a card to Make nice to have (or Make required), Copy as alternative, or Remove the credential.
Choose what to share
Click a card to open it. Under Choose what to share, tick the attributes you want to receive. For each ticked attribute you can:
- Make optional: the attribute is nice to have instead of required. You need at least two ticked attributes before you can make one optional, and a credential can have at most four optional attributes. Once that limit is reached, the control is disabled on the other attributes until you make one of them required again.
- + condition: type a Required value and press Enter. The attribute must then equal that value, for example
NL.
Use Add information by name to request an attribute that is not in the list, for example address.country.
What happens when you tick nothing depends on the credential format. For an SD-JWT VC you receive only what the issuer always discloses; for an mdoc only the document type; for a W3C credential the whole credential, because that format cannot share selectively. Issuer, validity dates, revocation status and the holder key are always included.
Trust and security
Click Trust and security on a card to open the settings for that credential. The closed card summarises them, for example "Proof of possession required · any issuer".
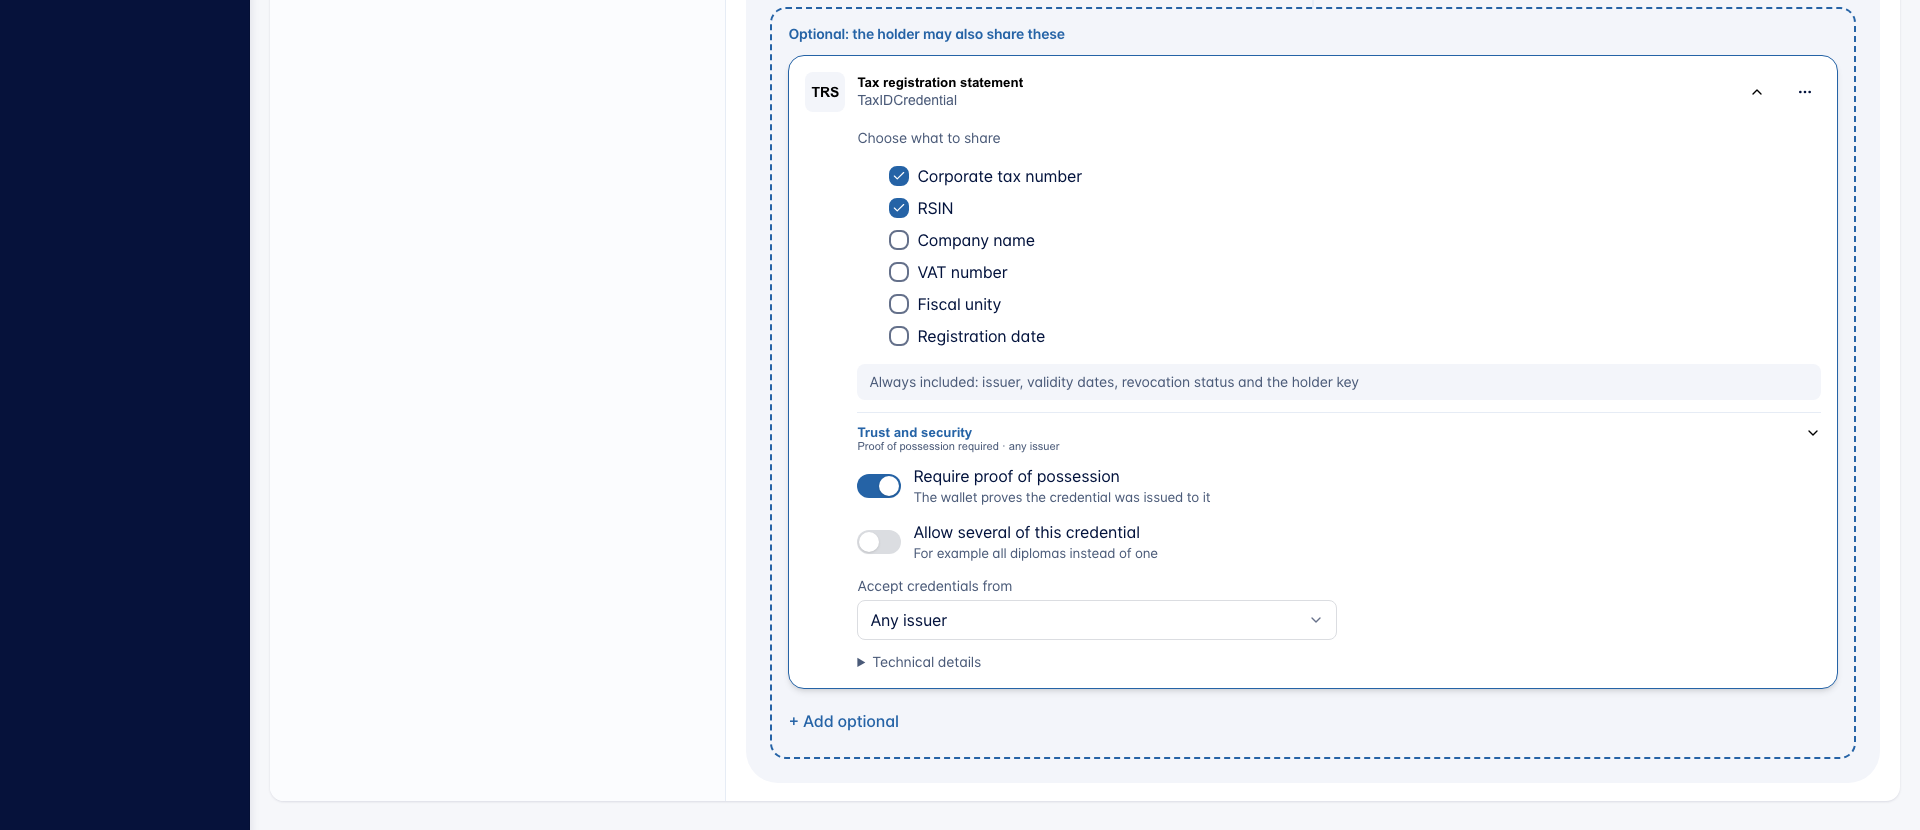
- Require proof of possession: the wallet proves that the credential was issued to it. This is switched on by default.
- Allow several of this credential: the holder may provide more than one credential of this type, for example all diplomas instead of one. When not set, only one credential of this type can be provided.
- Accept credentials from: which issuers you accept for this credential.
- Any issuer
- Issuers on a trusted list: choose a trusted list or paste its Trusted list URL. Click Manage trusted lists to add one; see Trusted issuers.
- Members of a federation: enter the Trust anchor of the federation.
- A specific certificate authority: enter its Authority key identifier.
Open Technical details to see or change the Response key, Format and Type of the credential. The type is the vct for an SD-JWT VC, the doctype for an mdoc and the type for a W3C credential.
The visual builder produces a DCQL query. If a credential needs something the builder cannot express, use the JSON view.
Edit the query as JSON
Click JSON next to What should the wallet share? to see and edit the request as a dcql_query.json document. The editor shows whether the document is currently ✔ Valid JSON or ✖ Invalid JSON.
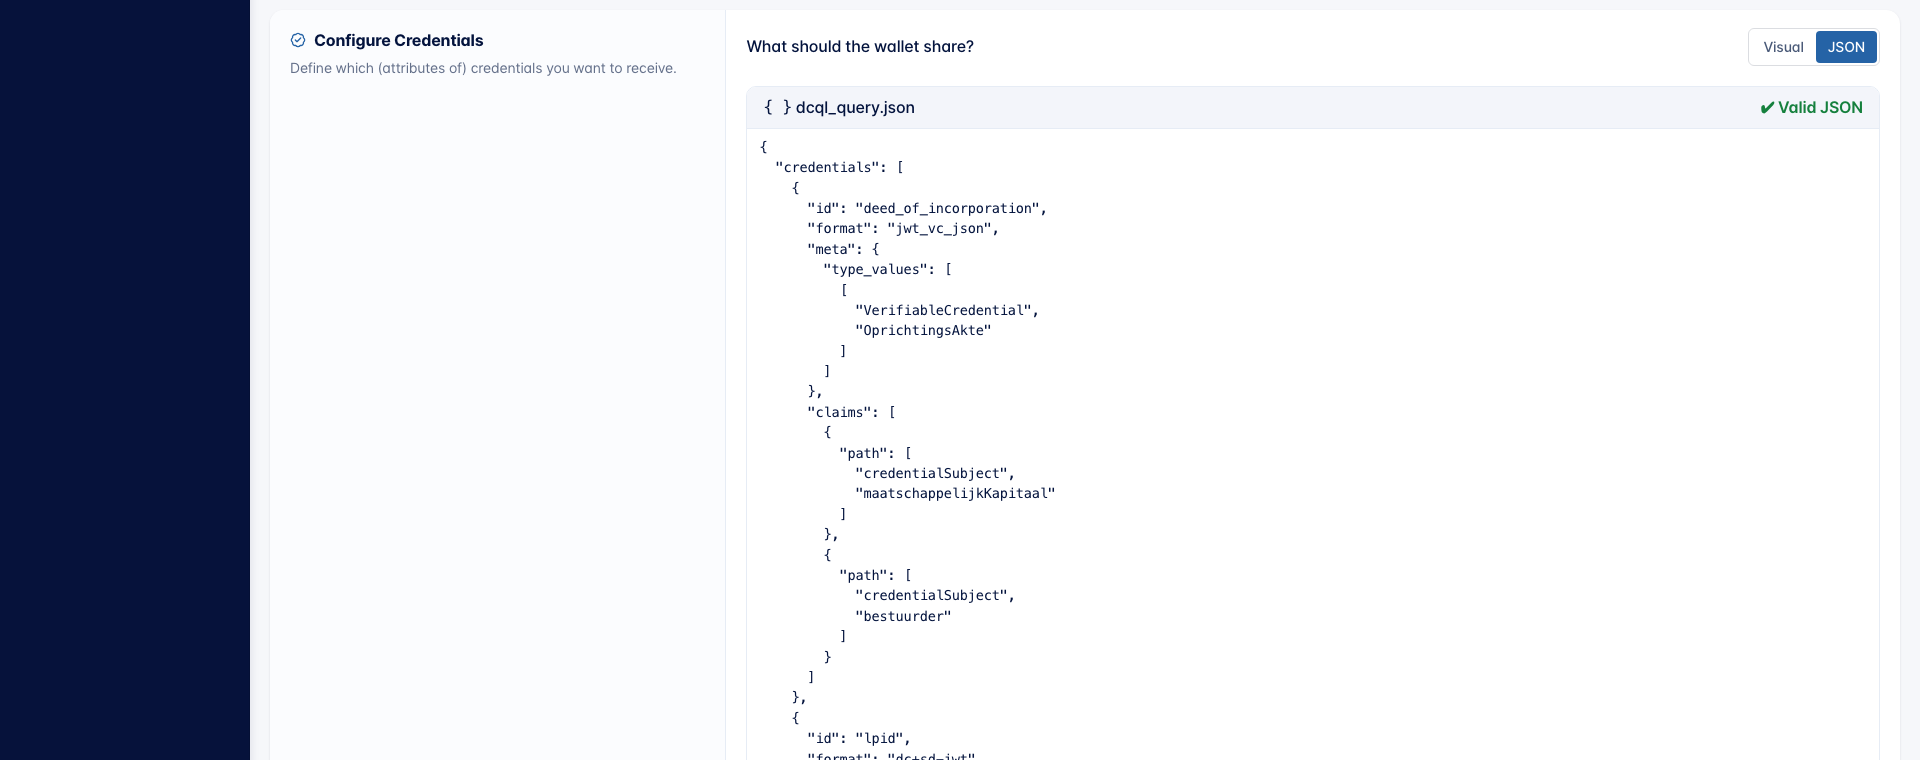
Click Visual to go back to the builder. A request that the builder cannot express, such as custom claim combinations, can only be edited as JSON.
Save
Click Save configuration at the bottom of the form to apply your changes, or Cancel to discard them. A "Save to apply changes" hint appears when you have unsaved edits.
Test the template
Once the template is saved, use Test in the top-right of the form to run a real verification request against it, without writing any code.
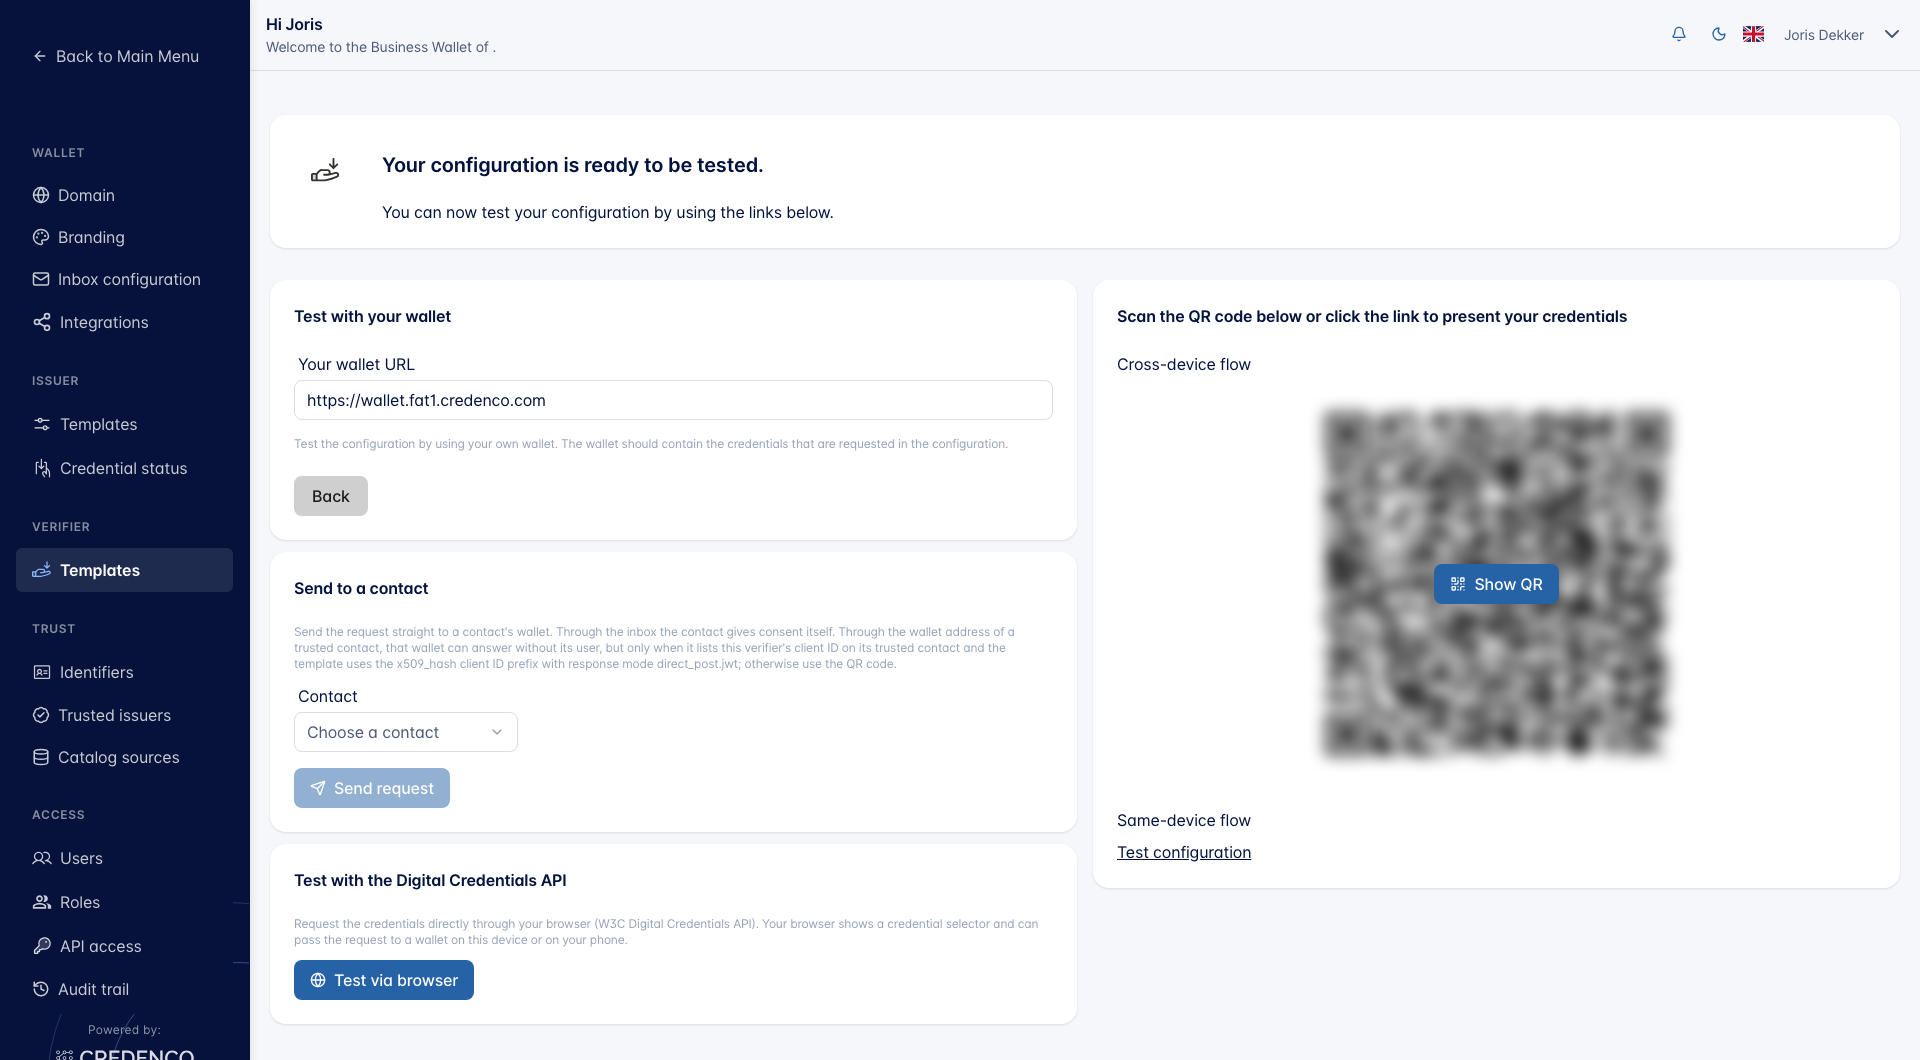
The test screen offers three ways to run the request:
- Test with your wallet: the right-hand card shows both flows. Click Show QR and scan the QR code with a wallet on another device, typically a phone (cross-device flow), or click Test configuration under Same-device flow to open the request in a wallet on this device.
- Send to a contact: choose a Contact and click Send request to send the request straight to that contact's wallet. Through the inbox the contact gives consent itself. Through the wallet address of a trusted contact, the wallet can answer without its user, but only when it lists this verifier's client ID on its trusted contact and the template uses the
x509_hashclient ID prefix with response modedirect_post.jwt; otherwise use the QR code. The screen reports whether the request was delivered and is waiting for the answer, whether the wallet did not accept it directly, or whether the wallet could not be reached. - Test with the Digital Credentials API: click Test via browser to request the credentials through your browser. The browser shows a credential selector and can pass the request to a wallet on this device or on your phone. This needs a recent version of Chrome or Edge.
Your wallet URL controls which wallet the same-device request is sent to. It defaults to the Business Wallet you are signed in to, and is not needed when you scan the QR code. That wallet must actually hold the credentials your template asks for, otherwise there is nothing to present.
If the wallet does not answer within 5 minutes, the screen reports that there was no response and you can try again.
Present the credentials
The wallet shows a consent screen listing every credential it holds that matches the template.
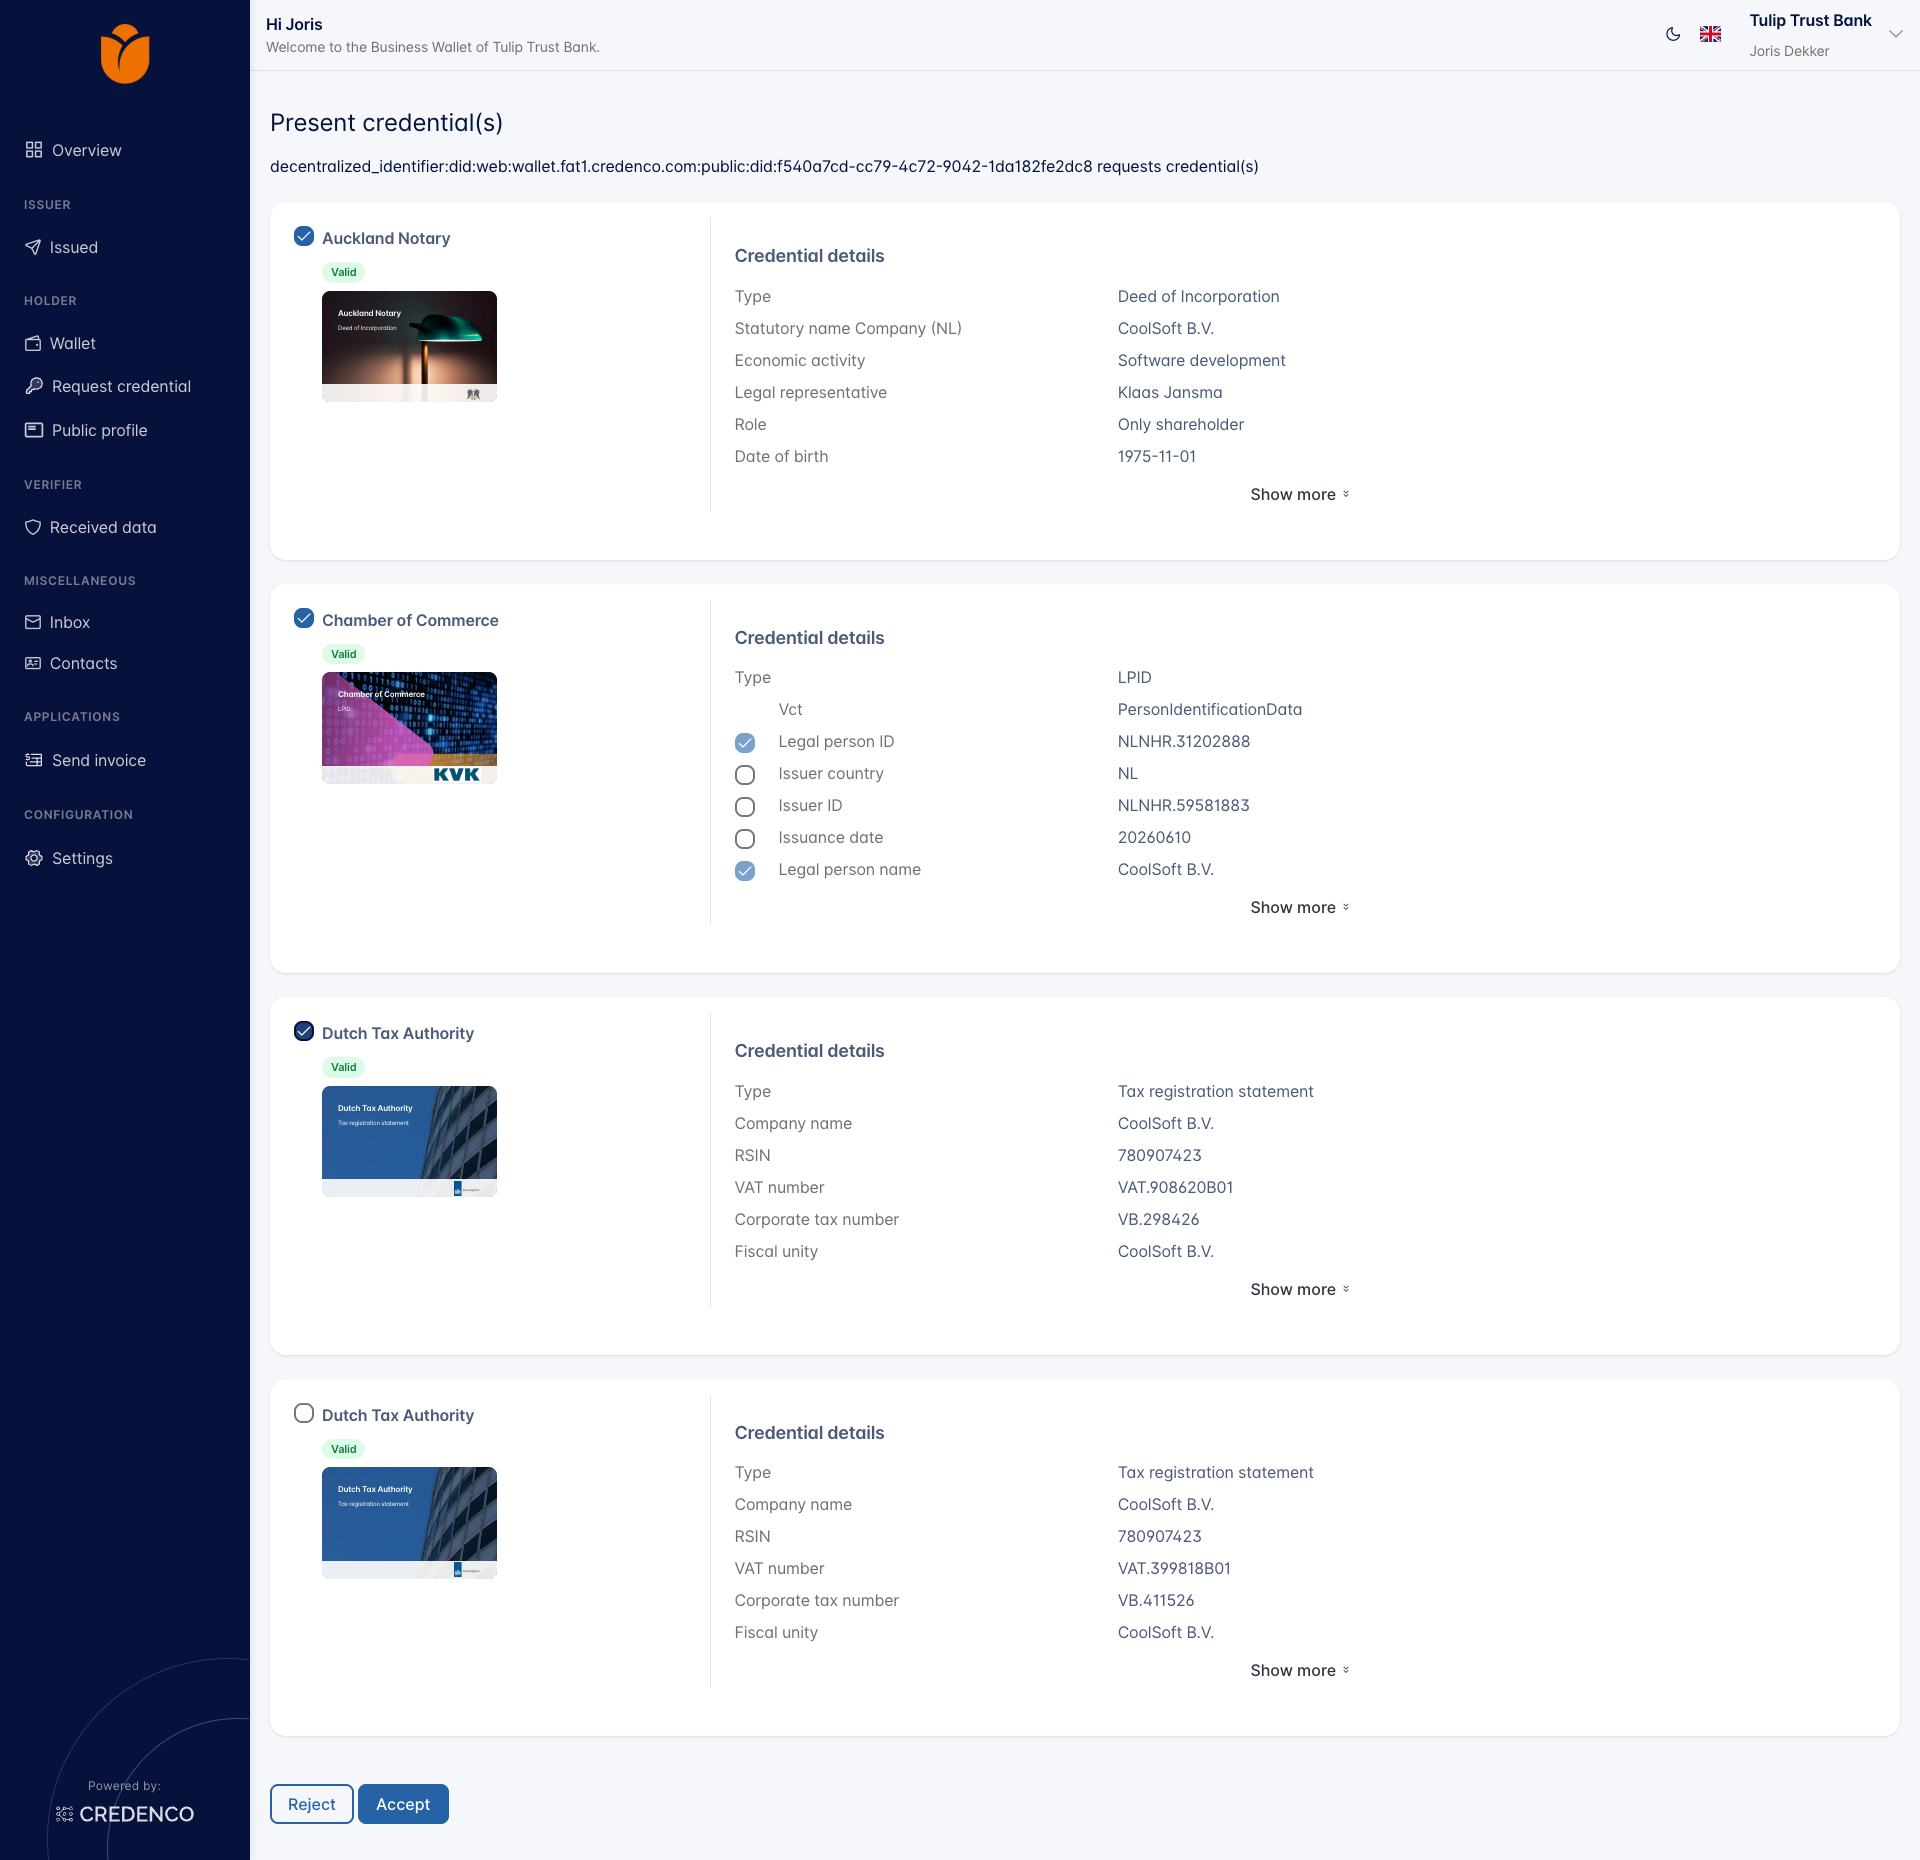
Each card shows the issuer, a Valid badge, and the credential details. Tick the credential(s) you want to present, then click Accept. Accept stays disabled until you select at least one credential.
For credentials that support selective disclosure, the individual attributes have their own checkboxes. The attributes your template marked as requested are pre-selected and locked; the rest are optional and you can add them. Use Show more to see the remaining attributes.
Click Reject to refuse the request instead.
Read the result
After accepting, the test screen reports the outcome.
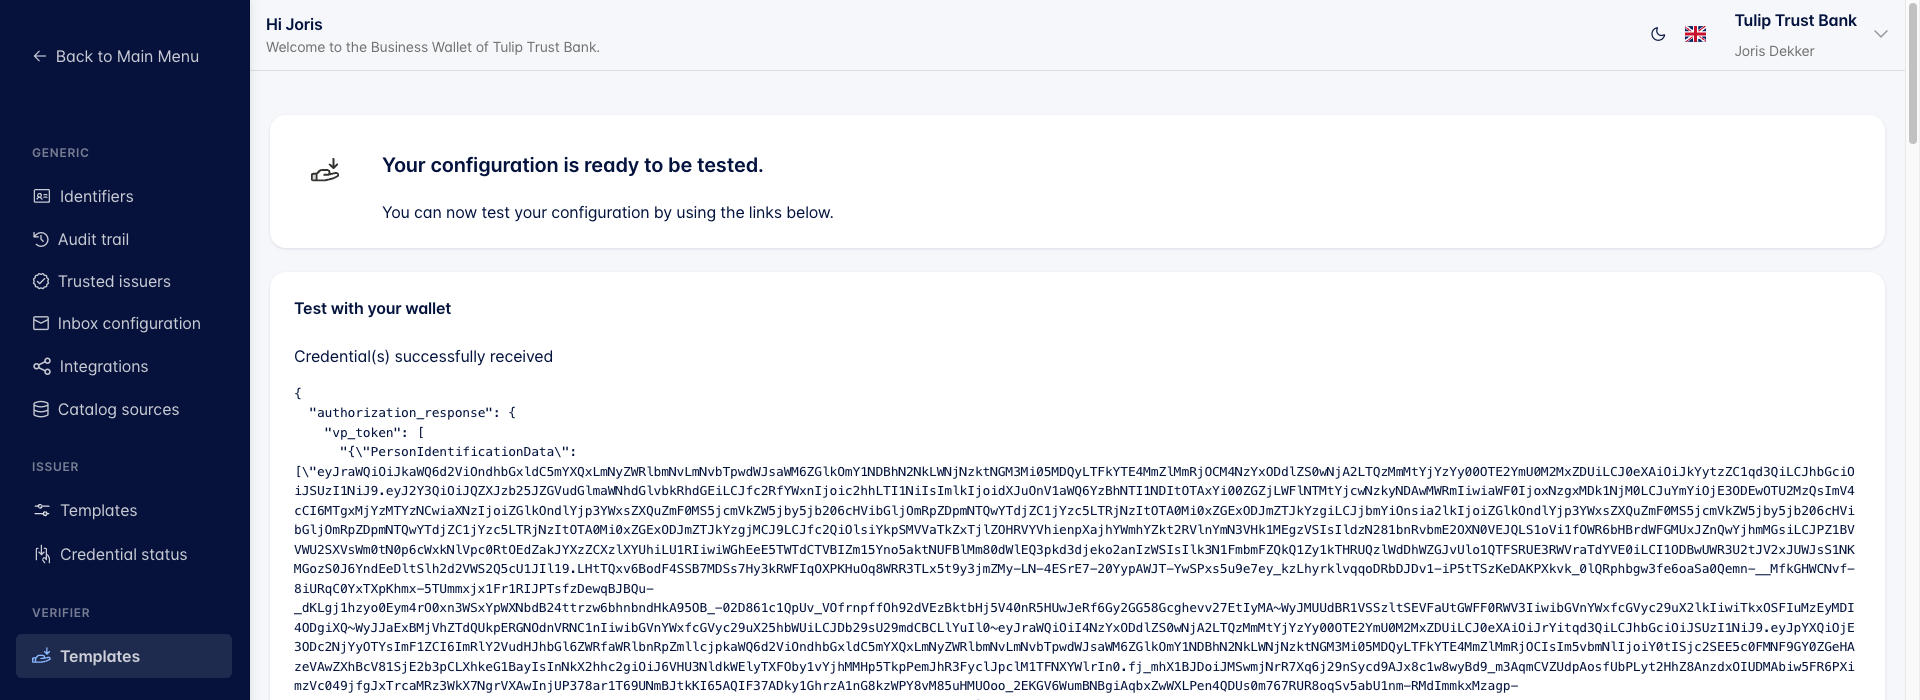
Credential(s) successfully received means the presentation passed every policy you enabled. Below the message the full authorization_response is shown, including the raw vp_token and the decoded credential_claims. This is the same payload your own backend receives from the Universal OIDC4VP API, so it is a good way to check which attribute names and values you will actually get.
A test run is a real verification. The result is stored like any other, under Verifier → Received data.
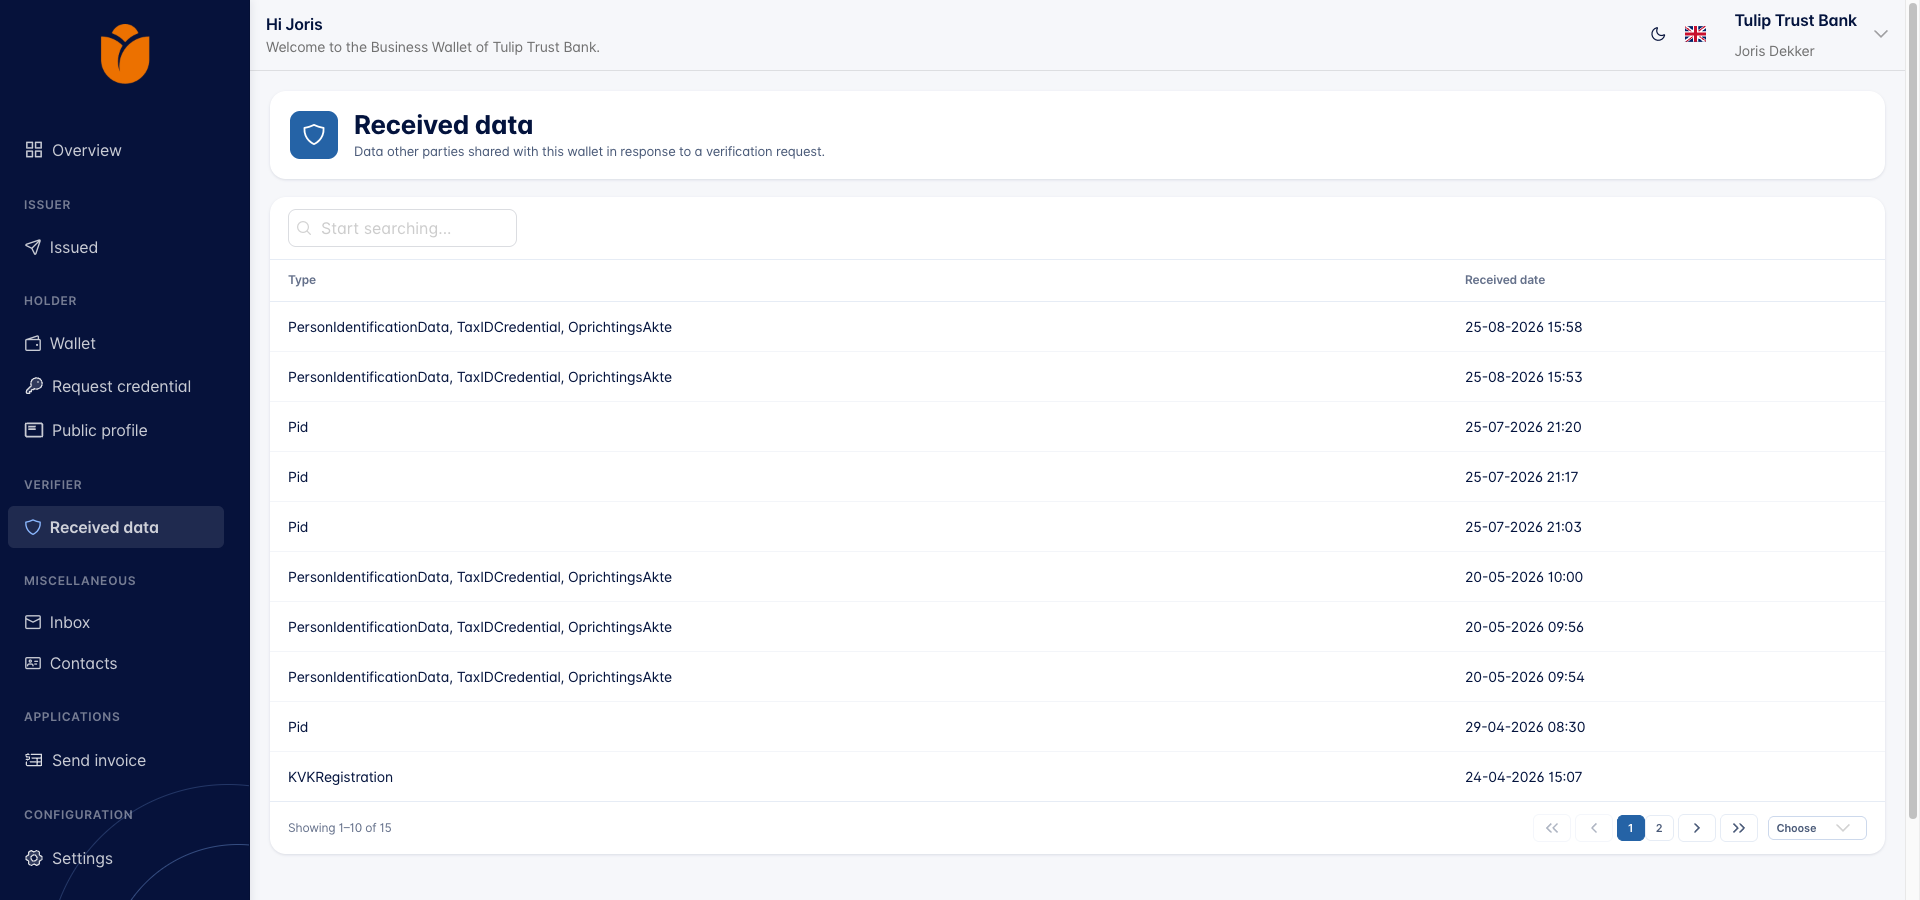
Testing does not use your Success URL or Error URL. Those apply only when a verification is started from your own application.
You need the Verifier templates (Change) permission to create, edit, or delete verifier templates.